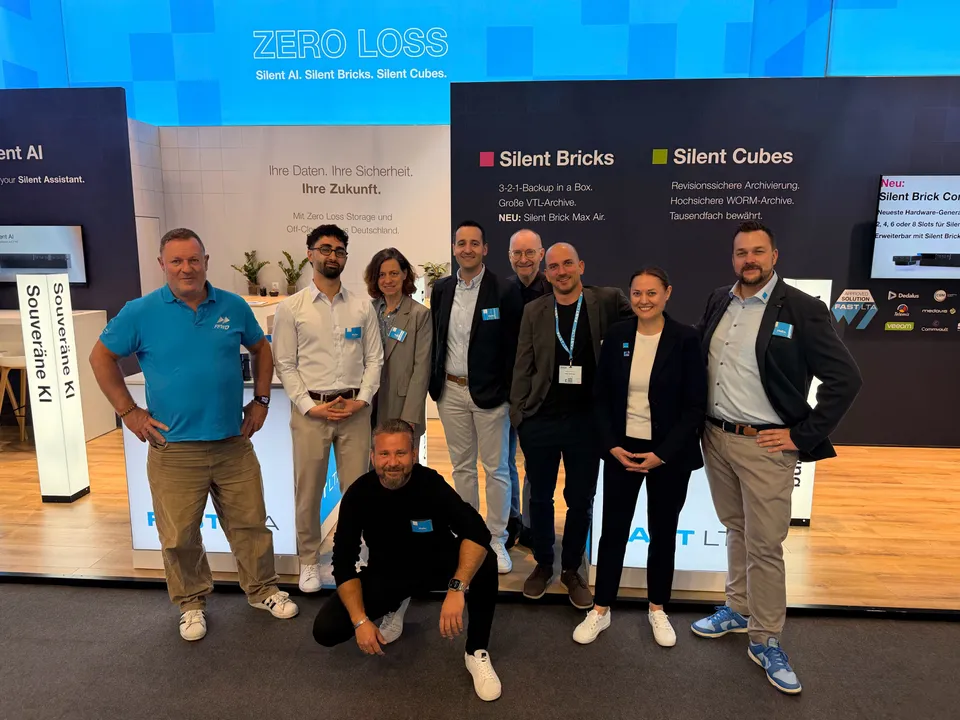
Hello. We are FAST LTA.

Our products and services help our SME clients to simplify data backup and migration, minimise legal and regulatory risks associated with the storage and use of sensitive data, and reduce the long-term risk of data loss.

Over 2,500 customers rely on our solutions
HAHN Automation Group Logo 2c fs WEB | FAST LTA
Logo mrws goss rgb | FAST LTA
WMU Weser Metall Umformtechnik Gmb H | FAST LTA
Wiberg AG | FAST LTA
Universitätsklinikum Düsseldorf | FAST LTA
Verwaltungsgemeinschaft Neumarkt St Veit | FAST LTA
Terhalle Holding Gmb H | FAST LTA
Stadt Neustadt a Rbge | FAST LTA
Stadt Brandenburg an der Havel Leben | FAST LTA
Stadt Wittenberge | FAST LTA
STABILO International Gmb H | FAST LTA
Sahle Baubetreuungsgesellschaft mb H | FAST LTA
Spital STS AG Spital Thun | FAST LTA
Riedel Bau AG | FAST LTA
Radiologie Mayen | FAST LTA
Ortspolizeibehörde Bremerhaven | FAST LTA
Oberschwaben Klinik g Gmb H Sankt Elisabethen Klinikum | FAST LTA
Oldenburgische Landesbank AG | FAST LTA
Niederer Kraft Frey AG | FAST LTA
OW Rechtsanwaltsgesellschaft mb H | FAST LTA
Naabtaler Milchwerke Gmb H Co KG | FAST LTA
Landratsamt rosenheim | FAST LTA
Kreiskrankenhaus Prignitz Gmb H | FAST LTA
Krankenhaus Stiftung der Niederbronner Schwestern Sankt Vincentius Krankenhaus | FAST LTA
Kliniken Südostbayern AG | FAST LTA
Klinikum Nürnberg | FAST LTA
KIP Holding Gmb H Co KG | FAST LTA
KKB Josef farbe | FAST LTA
Josef Feldhaus Gmb H Co KG | FAST LTA
Kassenärztliche Vereinigung Westfalen Lippe KVWL | FAST LTA
Johann Dettendorfer Spedition Ferntrans Gmb H Co KG | FAST LTA
Johann Bunte Bauunternehmung Gmb H und Co KG | FAST LTA
Investitionsbank Schleswig Holstein | FAST LTA
IDEAL Automotive Gmb H | FAST LTA
Innflow AG | FAST LTA
Hellmann Worldwide Logistics SE Co KG | FAST LTA
GNS | FAST LTA
Handwerkskammer Halle Saale | FAST LTA
Frisch Faust Tiefbau Gmb H | FAST LTA
Georg Roth Stiftung Co Lebensmittelfilialbetrieb KG svg | FAST LTA
Flughafen München Gmb H | FAST LTA
Fendt caravan gmbh | FAST LTA
DLR Logo svg | FAST LTA
CLS New logo Générique CMJK | FAST LTA
CA AUTO BANK | FAST LTA
Atlas Copco EPS Gmb H | FAST LTA
Bergische Industrie und Handelskammer Wuppertal Solingen Remscheid | FAST LTA

Our Vision

We believe that every business has the right to retain full control over its data, without hidden dependencies, without unexpected usage-based costs, and without data being shared with third parties.

That is why we develop solutions that make exactly that possible: Zero Loss Storage and Off-Cloud AI. Turnkey, local, secure, and predictable.


Our values

What drives us

Images for corporate values 202605261645 | FAST LTA

Reliable

We stand by our promises. Our customers plan for terms of 10 years or more – and that requires partners they can rely on. No marketing promises that fall flat in practice. No subscription model that delivers surprises after purchase.

I need one more photorealistic 202605261617 | FAST LTA

Transparent

We communicate openly – both internally and externally. Our staff know what we’re working on and why. Our customers receive honest information rather than sales brochures. Regular company meetings aren’t just a nice-to-have for us; they’re an integral part of how we work.

I need three photorealistic images 202605261617 1 | FAST LTA

Sustainable

We treat the resources entrusted to us with care – whether that be our customers’ data, the energy consumed by our devices, or our employees’ time. Long-term solutions rather than short-term promises. Predictable total cost of ownership rather than spiralling subscription costs.

No Startup. But always innovative.

For over 20 years, we have been developing secure storage systems for regulated industries and users handling sensitive data. Starting with the idea of offering a truly uncompromisingly secure data storage solution for personal memories, we have developed many innovations over the years, resulting in three product ranges for secure data storage and usage, as well as a wealth of experience.

New Address

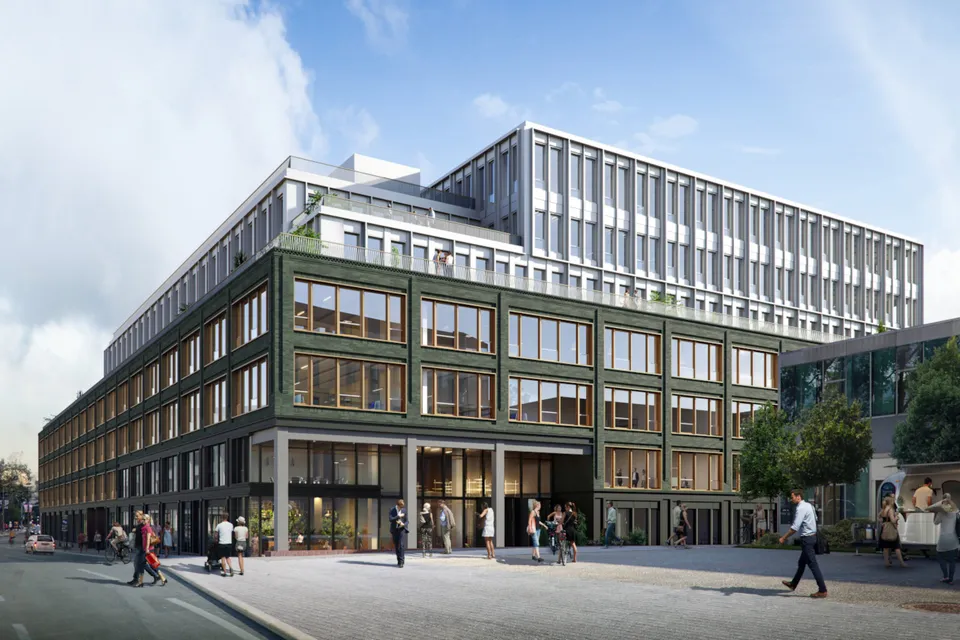
In mid-2026, after decades in Munich’s Westend district, FAST LTA will be moving to Tölzer Straße 1 in Obersendling. The new building is modern, open-plan and well-connected. All offices are on the same floor, and flexible workspaces encourage interaction between departments.

The third product range: Silent AI

Silent AI has been shipping since March 2026 and is being deployed by early customers. With increasing regulatory pressure and the growing prevalence of cloud AI, this local, data-sovereign AI appliance fills the gap that previously prevented the use of internal, sensitive or regulated data with available AI solutions.

Silent Brick Max Air

In January 2026, the first Silent Brick Max Air units will be delivered to customers. As the first storage medium of its kind, this extension for the Silent Brick system offers a true air gap without the need for physical media removal. The galvanic isolation of the storage media can be manually or automatically deactivated, enabling automated rotation scenarios.

Skaliert Bild Fabrikfinal | FAST LTA

New leadership

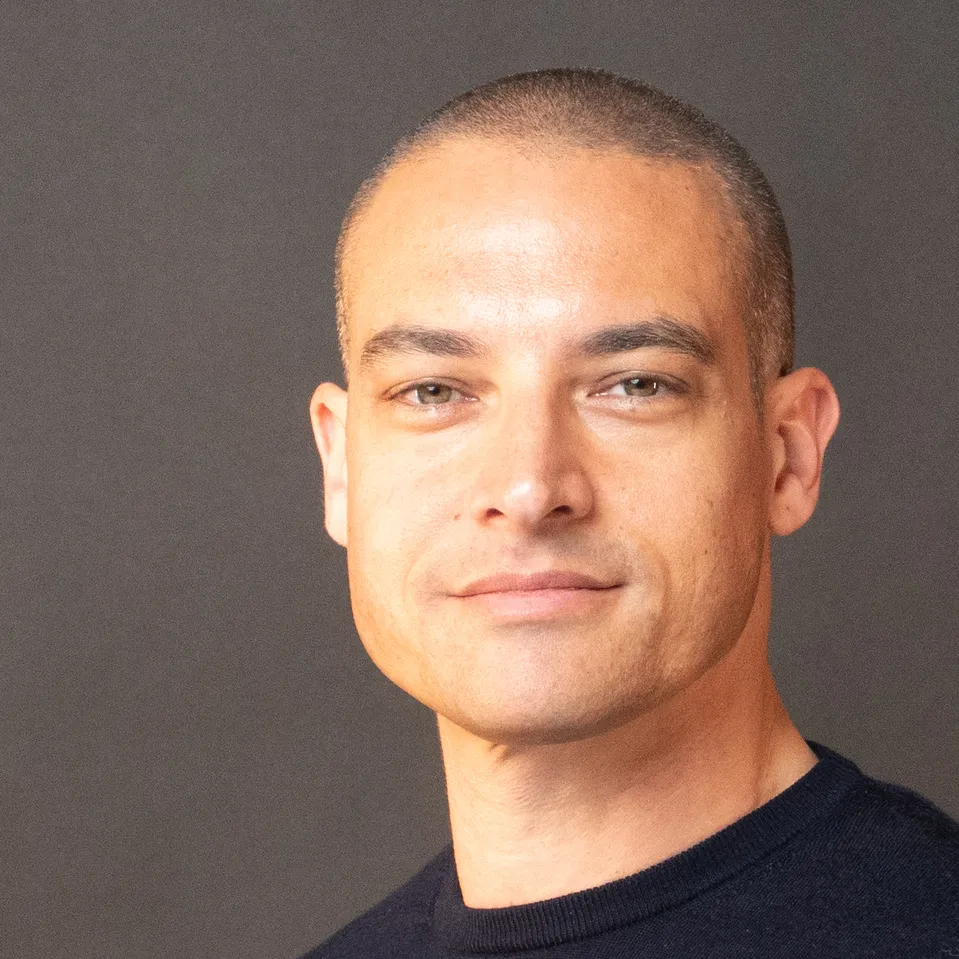
In early to mid-2025, Samir Fadlallah will take over as CEO and Roland Stritt will become CRO. Steffi Körner, the current CEO, will remain with the company in a sales role and on the executive board.

2025 04 Samir Fadlallah CEO FAST LTA Head | FAST LTA

New Investor

Summa Equity, a new investor, is acquiring FAST LTA’s shares from the previous owner, Afinum. The ‘impact investor’ aims to establish FAST LTA as the European leader in the ‘cyber security’ portfolio sector.

Introduction to Silent AI

The concept of a sovereign, appliance will be presented to the public for the first time at the company’s own event, FAST FORWARD 2024. The idea: in regulated industries or when dealing with sensitive data, the emerging but US-based generative AI offerings pose data protection challenges. Local alternatives are very expensive and complex. Silent AI relies on RAG without LLM training, which significantly reduces costs and complexity.

New: Silent Brick Pro & Controller X

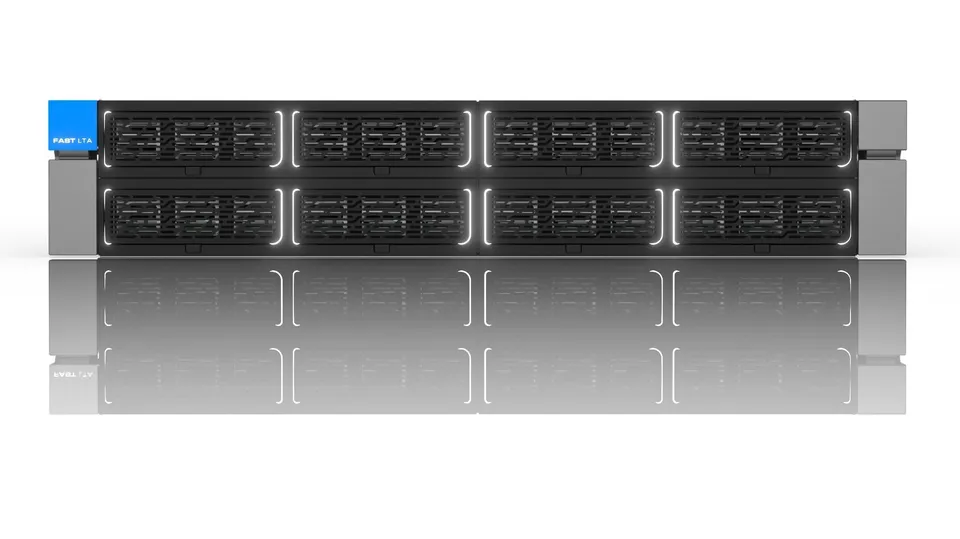
Following years of development, FAST LTA is presenting the new Silent Brick system. With fast NVMe storage (Silent Brick Pro) and external expandability, the storage system for backup and restore sets new standards in terms of performance, security and cost-effectiveness. Delivery will commence at the end of 2024.

X6080 | FAST LTA

Head Unit Pro

The head unit is also being updated. The new H1000 and H1000Pro models now support up to 10G Ethernet and integrate seamlessly into both existing and new systems.

Silent Cube DS

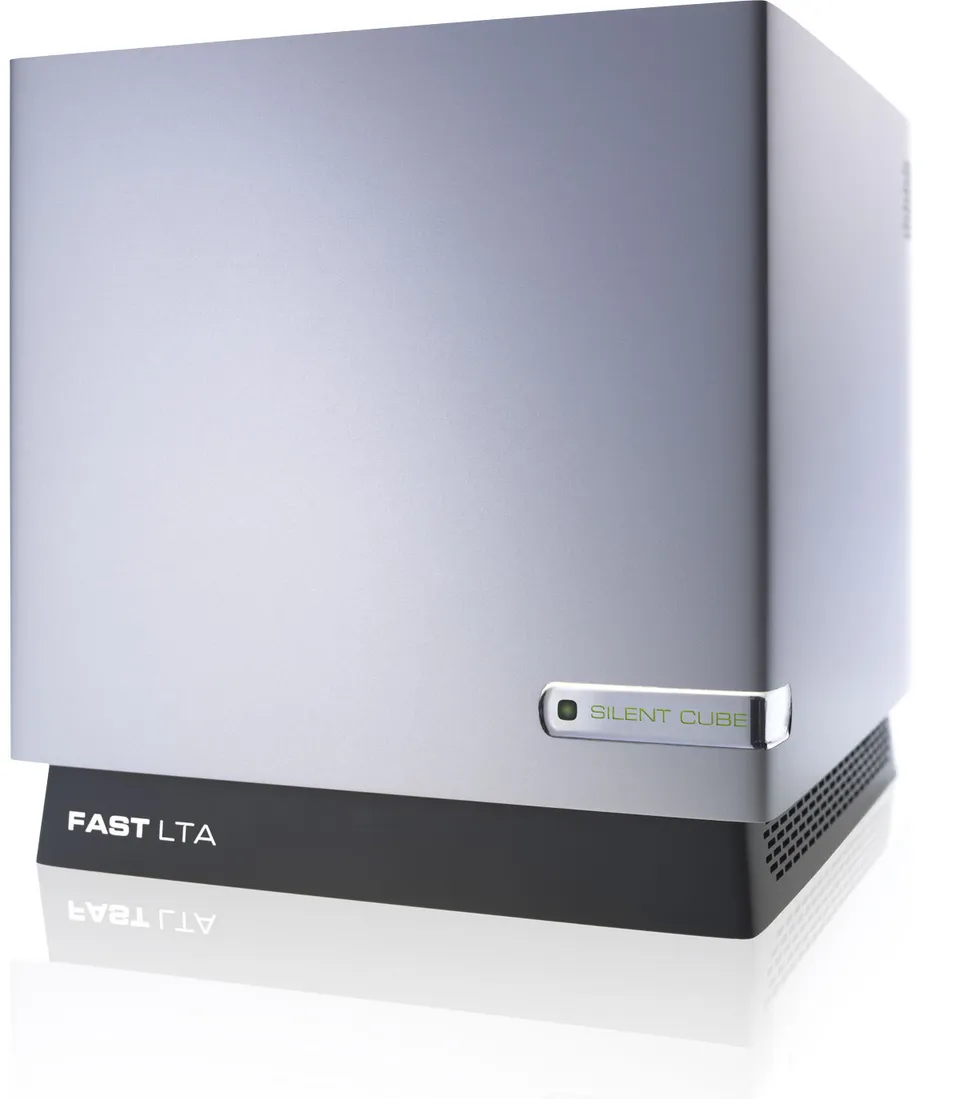
After an incredible 13 years, the Silent Cube is getting a successor: the Silent Cube DS and Silent Cube DS Pro. These can now be installed in a 1U rack space. The key feature, however, is full compatibility with existing Silent Cube systems. Original Silent Cubes can continue to be used, whilst new data runs on the more powerful Silent Cube DS (Pro).

Afinum Investments acquires FAST LTA

FAST LTA AG is being re-registered as FAST LTA GmbH. The new owner is focusing on the company’s growth in the German and European markets.

Head Unit for VMware®

Large-scale archive environments containing billions of files can now be implemented more effectively by virtualising the head unit. -sealed Silent Cubes continue to be used for long-term storage.

Silent Cube Compact

A head unit and long-term storage in a single compact device: that’s the new Silent Cube Compact. The ‘SCC’ is set to be a hit, particularly in public sector environments where data volumes and space are limited.

The first Silent Cube

The time has come. A major German hospital is the first customer for the brand-new Silent Cube. This cube securely stores data from imaging devices in an unalterable format for decades.

SC | FAST LTA

Management

Experts. A firm belief in small and medium-sized enterprises. No corporate structure.

FAST LTA employs specialists in data storage, IT security and AI – many of whom have been with the company for over a decade. Flat hierarchies, short lines of communication, and direct points of contact.

2025 04 Samir Fadlallah CEO FAST LTA Head | FAST LTA

CEO | Management Board

Samir Fadlallah

Samir Fadlallah took over as head of the company in the spring. Samir Fadlallah brings extensive management experience to the role. Most recently, he served as Chief Information Officer (CIO) and Chief Technology Officer (CTO) at the media group Axel Springer, where he also held the position of Head of Global Generative AI

Roland Stritt CRO FAST LTA | FAST LTA

CRO | Management Board

Roland Stritt

Roland Stritt has been Chief Revenue Officer, overseeing sales and marketing, since mid-2025. Roland Stritt brings over 20 years of extensive expertise in IT sales, sales leadership, channel management and technology. Most recently, he served as Vice President for Central EMEA at SentinelOne, where he had been responsible for the region’s operations since August 2022.

FAST LTA AG
www.fast-lta.deRüdesheimer Str. 11
80686 München
Telefon: +49 89 89 047-0
Telefax: +49 89 89 047-890
info@fast-lta.de | FAST LTA

VP Sales | Management Board

Stefanie Körner

Stefanie Körner joined FAST LTA in 2008 and has held a senior position in sales ever since. In 2019, following the company’s acquisition by Afinum, she took on the role of CEO and became a member of the management board, a position she still holds today.

FAST LTA AG
www.fast-lta.deRüdesheimer Str. 11
80686 München
Telefon: +49 89 89 047-0
Telefax: +49 89 89 047-890
info@fast-lta.de | FAST LTA

CTO | Management Board

Jörg "Ali" Adelstein

As Head of Development, Ali Adelstein is responsible for both innovation and the long-term security of FAST LTA’s products. Together with his team of hardware and software developers, he brings the company’s three product lines to life.

Careers

Join FAST LTA

We are expanding and are always looking for new team members. Whether you’re interested in a specialist career or a leadership role, we nurture talent and support career development, offer attractive benefits, and look forward to receiving your application.

IMG 3121 | FAST LTA
Blog Post | 2/3/2026
What Is Ransomware? Explained for IT Decision-Makers
Ransomware is malicious software that encrypts or locks data and systems, then demands a ransom for their release. The name says it all: ransom plus software. For IT decision-makers, one insight matters most: modern ransomware is not just a security problem. It is a business threat that causes downtime lasting days to weeks, sometimes longer.The threat is persistent. The Veeam Ransomware Trends Report 2025 found that roughly seven out of ten organisations were attacked within a year, and 89 percent of those attacks targeted backup repositories. According to the Sophos State of Ransomware 2025, 49 percent of organisations whose data was encrypted paid the ransom.This article explains what ransomware is, how it has evolved, and why traditional prevention alone is not enough.---
Blog Post | 3/20/2026
Multi-Tier Backup Architecture: Best Practices 2026
The idea that "backup = one copy on external hardware" is sufficient is no longer defensible in 2026. Ransomware attacks backups just as aggressively as production systems: the Veeam Ransomware Trends Report 2025 found that 89 percent of attacks targeted backup repositories. A modern backup architecture requires multiple tiers that are isolated from each other and offer different trade-offs between performance, cost, and security.The 4-tier model is the practical standard for cyber resilience, and it maps directly onto what the NIS2 Directive (Directive (EU) 2022/2555) demands: backup management, disaster recovery, and crisis management as mandatory risk measures.---
Blog Post | 2/26/2026
Banking IT Regulation and Cloud: What Banks Need to Know About Data Storage Compliance
European banks operate under a layered regulatory framework for IT and cloud use. Since 17 January 2025, the EU layer is dominated by DORA (Regulation (EU) 2022/2554), which applies directly in all member states and sets binding requirements for ICT risk management, backup, and third-party arrangements. The EBA Guidelines on outsourcing arrangements add the supervisory expectations for outsourcing, including cloud. On top sit national rules: in Germany, for example, BaFin's BAIT circular (Banking Supervisory Requirements for IT) operationalised §25a of the German Banking Act for years; since January 2025, DORA has superseded much of its substance, with national rules retaining a supplementary role.The practical consequence for any IT decision-maker at a European bank: if you use cloud services for data storage or backup, you must be able to demonstrate that the institution retains full control over its data at all times. This guide explains what the framework concretely requires for data storage, what conditions apply to outsourcing agreements, and why on-premises remains the regulatorily safer strategy for many institutions.**Reading time:** approx. 9 minutes | **Updated:** May 2026---
Blog Post | 3/10/2026
Tabletop Exercise Ransomware: Instructions and Scenarios
A tabletop exercise is a crisis simulation at the conference table: no real attack, no real systems, but real decisions, real communication chains, and real gaps that surface.For ransomware scenarios, the tabletop exercise is particularly valuable because it forces exactly the questions that must be answered under time pressure during an actual incident: Who decides whether to pay a ransom? How do we report the incident to the competent authority within the NIS2 deadlines? How do we recover if the DR plan folder is also encrypted?This guide covers preparation and facilitation, including three complete scenarios with discussion questions and an evaluation framework.**Reading time:** approx. 13 minutes | **Updated:** May 2026---
Blog Post | 5/21/2026
Assume Breach: The Design Principle That Changes Your Architecture
"Assume Breach" is not just a security slogan. It is a fundamental design principle that reshapes the entire architecture of an organization. Think it through consistently, and you have to rebuild parts of your IT.The concept is simple: **not if, but when will your organization be attacked and compromised?**This is not pessimism. The data is unambiguous: in the Veeam Ransomware Trends Report 2025, roughly 7 in 10 organizations reported at least one ransomware attack in the preceding year, despite improved defenses. For exposed industries (financial services, healthcare, manufacturing), the question is realistically only: when?---
Blog Post | 2/11/2026
Compliance with WORM Storage: What External Financial Auditors Expect
Every year, external financial auditors examine the annual accounts of companies across the EU. The statutory audit, harmonised by the EU Audit Directive (2006/43/EC, as amended), is conducted under International Standards on Auditing (ISA). One part of that audit regularly catches IT departments off guard: the auditor's assessment of the systems that store accounting records. If archived records can be altered or deleted, the auditor cannot rely on them as evidence.This article explains what auditors actually check in your archiving systems, why WORM storage (Write Once Read Many) has become the reference answer, and what documentation you should have ready before the audit team arrives.---
Blog Post | 3/3/2026
Creating an Incident Response Plan: Template and Guide
An incident response plan (IRP) is the backbone of resilience. It is the document that prepares your organization for a cyberattack before it happens. A well-structured IRP significantly reduces response time and minimizes the extent of damage. Yet many organizations have none, or only an outdated concept that nobody has tested.Under the NIS2 Directive (Directive (EU) 2022/2555), incident handling is an explicit risk management requirement for essential and important entities. Here is a concrete template with 8 required sections that every IR plan must have.---
Blog Post | 5/12/2026
The 5 Pillars of IT Resilience: A Practical Framework
A robust IT resilience strategy does not rest on a single pillar. It rests on five. Each pillar has specific technologies, processes, and responsibilities. Many organizations invest heavily in Pillar 1 (Prevention) and neglect the other four. That is a classic mistake that leads to vulnerability, and it is also a compliance gap: NIS2 (Directive (EU) 2022/2555) explicitly requires backup management, disaster recovery, and crisis management alongside preventive measures.Here is a practical framework showing what belongs to each pillar and how to implement it.---
Blog Post | 1/7/2026
NIS2 Explained: Who Is Affected and What Do You Need to Do?
NIS2 is here. Directive (EU) 2022/2555 on network and information security applies across the European Union. Member states had to transpose it into national law by 17 October 2024. Many did so on time, some later: Germany, for example, brought its implementation act (NIS2UmsuCG) into force on 6 December 2025, without a general transition period. The result across the EU: tens of thousands of organisations must implement concrete IT security measures. Those that do not risk fines of up to EUR 10 million or 2% of global annual turnover.This article explains who is affected, what the directive requires, and what you need to do now.---
Blog Post | 4/15/2026
Audit-Proof Archiving vs. Immutability: The Difference Matters
A common misconception: "We use WORM storage, so we have audit-proof archiving." That is incorrect. Immutability is a necessary but not sufficient condition for audit-proof archiving.**Immutability** is the technical property that data cannot be deleted or altered after writing.**Audit-proof archiving** is the business and legal guarantee that an auditor or regulator can find, read, verify, and understand the data throughout the retention period.The distinction is critical, and it costs companies real money when they discover it during an audit.---